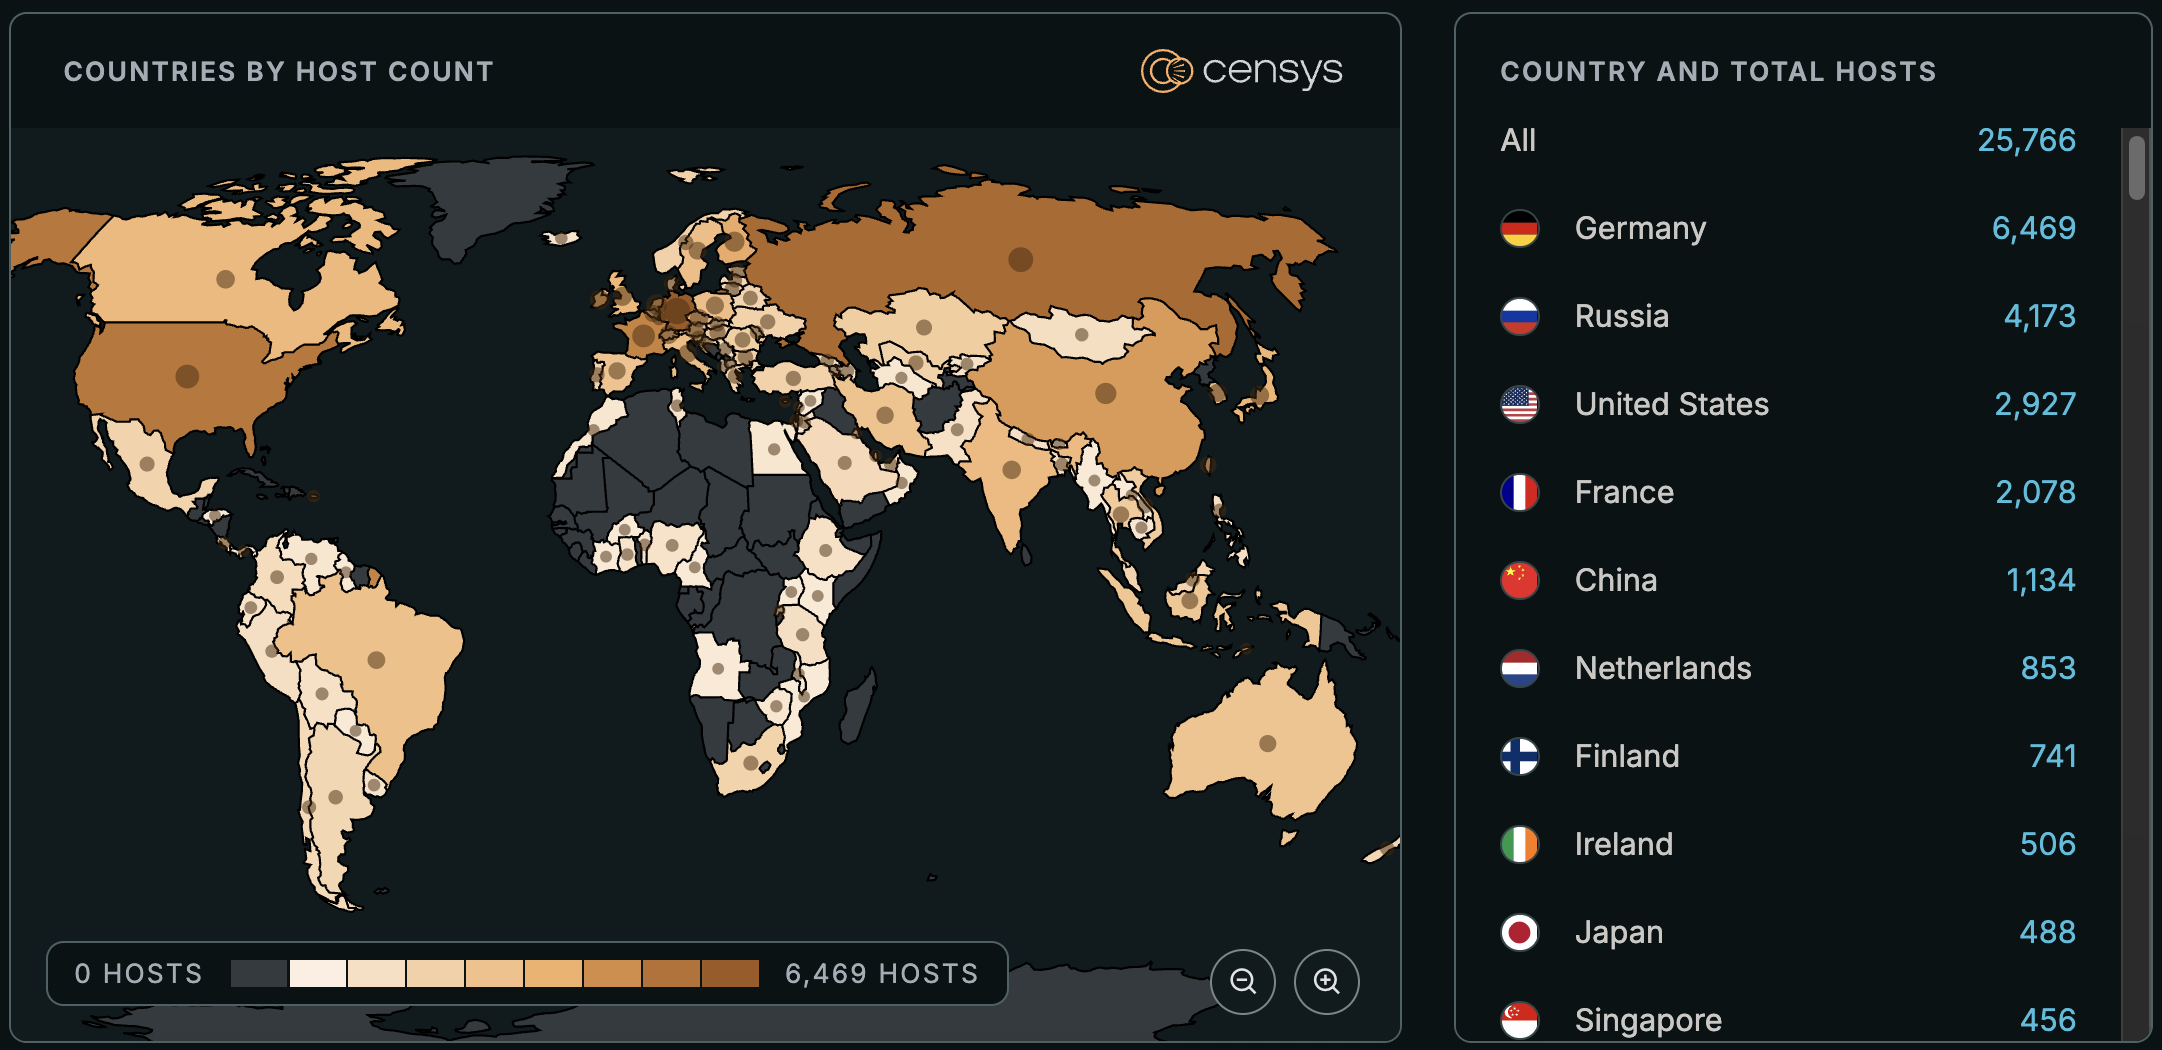
CVE-2026-97229 is an integer overflow in the CI/CD regular expression compiler of GitLab Community Edition and Enterprise Edition, CVSS 10.0, that allows an unauthenticated attacker to execute arbitrary code on the GitLab server. Although GitLab’s advisory says the flaw “under certain conditions, could have allowed an unauthenticated user to execute arbitrary code on the GitLab server via a specially crafted regular expression in a CI/CD configuration, due to insufficient regular expression validation,” neither GitLab nor NVD has published what those conditions are. GitLab fixed the issue on October 12, 2026 in versions 19.2.8, 19.3.5, and 19.4.2. Censys currently detects 25,766 hosts and 79,224 web properties with a version of GitLab affected by this vulnerability.
Details
| CVE ID | CVE-2026-97229, CVSS v3.1 10.0 (Critical) |
| Date of Disclosure | October 13, 2026 |
| Affected Assets | Self-managed GitLab CE and EE. GitLab.com is already patched. |
| Vulnerable Software Versions | 19.2.0 through 19.2.7 19.3.0 through 19.3.4 19.4.0 through 19.4.1 |
| PoC Available | Rapid7 published a proof-of-concept on October 13, 2026. |
| Exploitation Status | Not listed in the CISA Known Exploited Vulnerabilities (KEV) catalog as of writing. |
| Patch Status | GitLab released 19.2.8, 19.3.5, and 19.4.2 on October 12, 2026. |
Affected Assets
GitLab’s advisory lists the affected versions as “all versions from 19.2 before 19.2.8, 19.3 before 19.3.5, and 19.4 before 19.4.2.” That gives three affected ranges, each with its own patched version:
- 19.2.0 through 19.2.7, fixed in 19.2.8
- 19.3.0 through 19.3.4, fixed in 19.3.5
- 19.4.0 through 19.4.1, fixed in 19.4.2
The advisory covers self-managed GitLab CE and EE. GitLab.com is already running the patched version.
Censys Query
We currently detect 82,454 hosts and 205,541 web properties running GitLab, based on the following query:
(
  host.services.software: (vendor: "gitlab" and product: "gitlab")
  or web.software: (vendor: "gitlab" and product: "gitlab")
)
and not labels: "HONEYPOT"
Of these, 25,766 hosts (31%) and 79,224 web properties (39%) are running a vulnerable version according to this query:
(
  host.services.software: (
    vendor: "gitlab" and product: "gitlab"
    and ((version >= "19.2.0" and version <= "19.2.7")
      or (version >= "19.3.0" and version <= "19.3.4")
      or (version >= "19.4.0" and version <= "19.4.1")))
  or web.software: (
    vendor: "gitlab" and product: "gitlab"
    and ((version >= "19.2.0" and version <= "19.2.7")
      or (version >= "19.3.0" and version <= "19.3.4")
      or (version >= "19.4.0" and version <= "19.4.1")))
)
and not labels: "HONEYPOT"
PoC Available?
Rapid7 published a proof-of-concept for CVE-2026-97229 on October 13, 2026.
Exploitation Status
CVE-2026-97229 is not listed in the CISA KEV catalog as of October 13, 2026 and the Censys ARC team is not aware of exploitation in the wild. GitLab’s advisory does not mention whether the flaw has been exploited.
Patch Status
GitLab fixed the issue in 19.2.8, 19.3.5, and 19.4.2, released October 12, 2026 in a critical patch release. If you are running an affected version, we recommend:
- Upgrading to the fixed release for your branch: 19.2.8, 19.3.5, or 19.4.2.
- If an immediate upgrade is not possible, restricting inbound access to the GitLab web interface.